Agentic AI can support FDCPA-related controls by checking account and contact conditions before outreach, selecting an approved next step, and routing uncertainty for review. Whether the FDCPA applies depends on the debt, the parties, and the conduct. AI does not determine legal scope or guarantee compliance.
This guide is for U.S. servicing and collections teams. It explains how to map rule applicability, enforce outreach controls before a call or message, handle consumer responses, and keep workflow decisions reviewable.
Key takeaways
- Map the debt, collector role, jurisdiction, channel, and account status before choosing the rule set.
- Run contact permissions, preferences, timing, cadence, and data checks at the send or dial point.
- Keep AI actions inside approved content, payment, and negotiation limits.
- Route disputes, stop requests, wrong-party signals, hardship, and uncertainty to defined workflows.
- Preserve decision evidence and test controls across real systems, vendors, and channels.
How can agentic AI support FDCPA compliance?
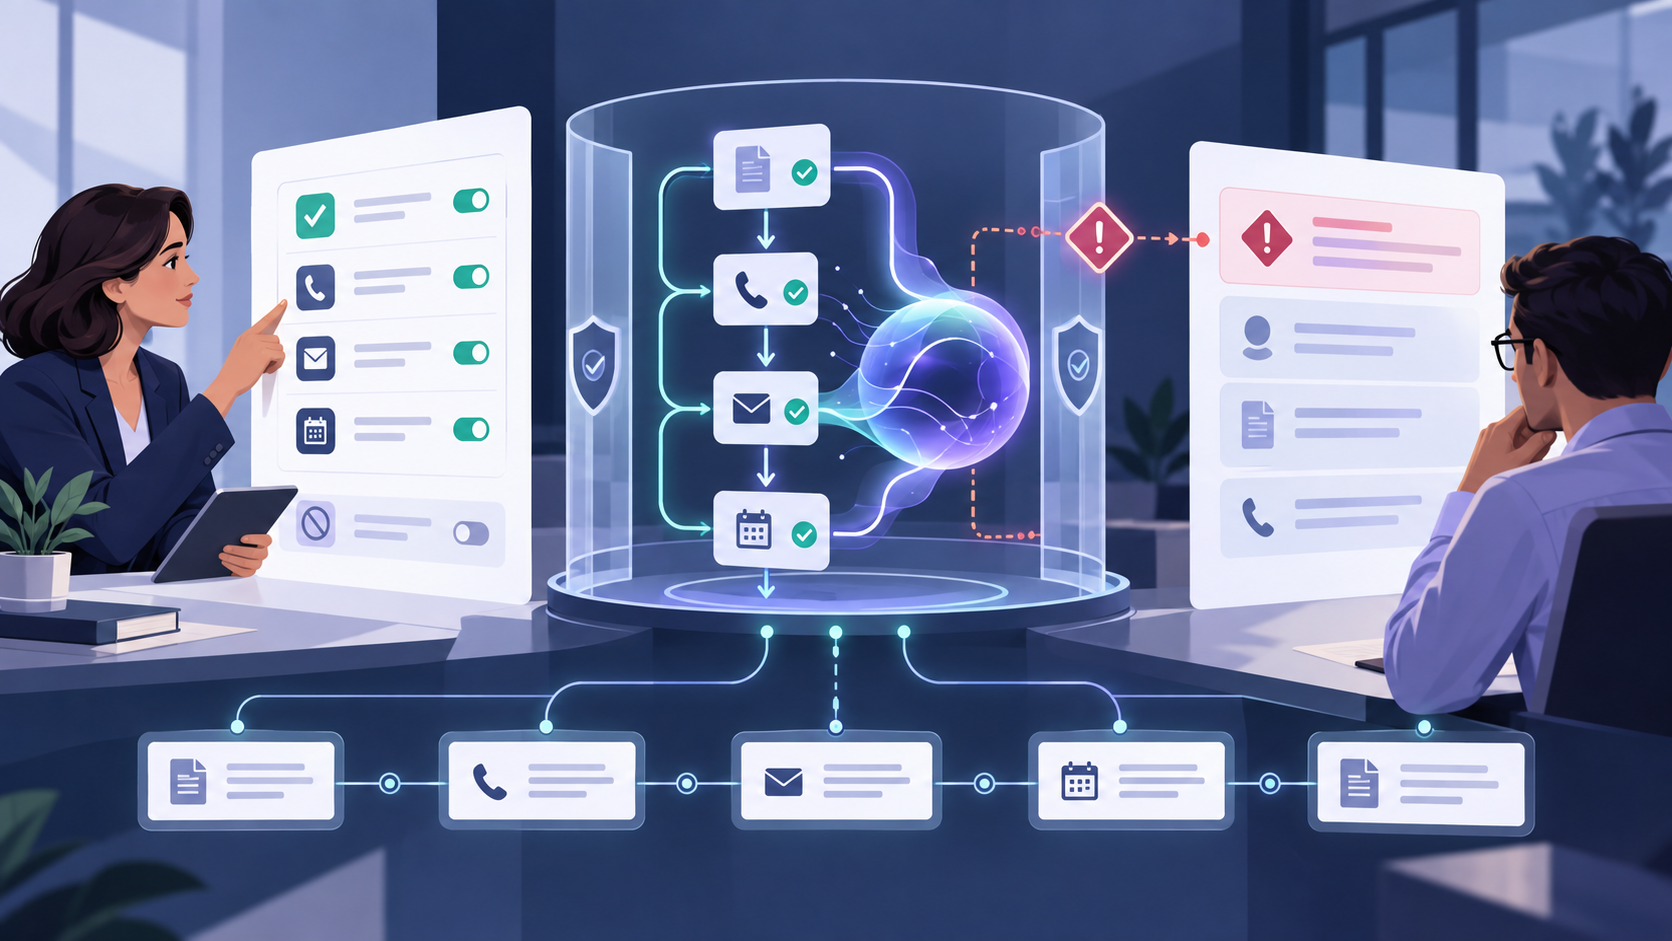
At runtime, an agent may interpret a response, select from permitted next steps, carry context across channels, and complete routine workflow actions. The organization must define the actions it may take and the conditions that require it to stop.
A safe operating model separates policy ownership from policy execution. Compliance and legal teams determine the applicable requirements and approve the policy. Operations translates that policy into account eligibility, contact rules, scripts, payment authority, exceptions, and review steps. The AI follows the approved workflow, while the system logs each action and its outcome.
This is an implementation guide, not a claim that FDCPA rules cover every collections operation. For the broader U.S. bank readiness view, see how banks can govern AI collections compliance.
Which U.S. rules should a collection team map first?
Start with the account and the role of each organization in the workflow. The FDCPA applies to covered debt collectors collecting consumer debts. An original creditor collecting its own debt is generally outside the FDCPA definition, but exceptions and the role of a vendor or affiliated entity can change the analysis. Use counsel to map the parties, debt type, account stage, communication, and state before a strategy goes live. The CFPB explains the original-creditor distinction, and the FTC publishes the FDCPA text.
For covered debt collectors, Regulation F implements the FDCPA. Its call-frequency presumptions are about telephone calls concerning a particular debt. They are not a universal safe harbor, a limit on every channel, or a default rule for every first-party creditor. The CFPB’s Regulation F text and sections on communications and call frequency are the primary references. Covered electronic collection communications also need a reasonable and simple opt-out method under the rule.
For covered debt collectors, a written dispute received during the validation period generally requires collection of the debt, or disputed portion, to stop until the collector sends verification or a judgment. The workflow should capture the receipt date, channel, validation status, amount disputed, and required next step. See the CFPB’s dispute rule, § 1006.38.
Other requirements may govern the same workflow. The TCPA and FCC rules can apply to calls using artificial or prerecorded voices. The FCC has determined that AI-generated voices fall within that category, while the consent analysis depends on the call, its purpose, and applicable exceptions. Review the FCC’s AI voice ruling with counsel. State collection laws may cover additional actors or impose different requirements. Payment activity, credit reporting, privacy, contracts, and internal policies may add controls of their own.
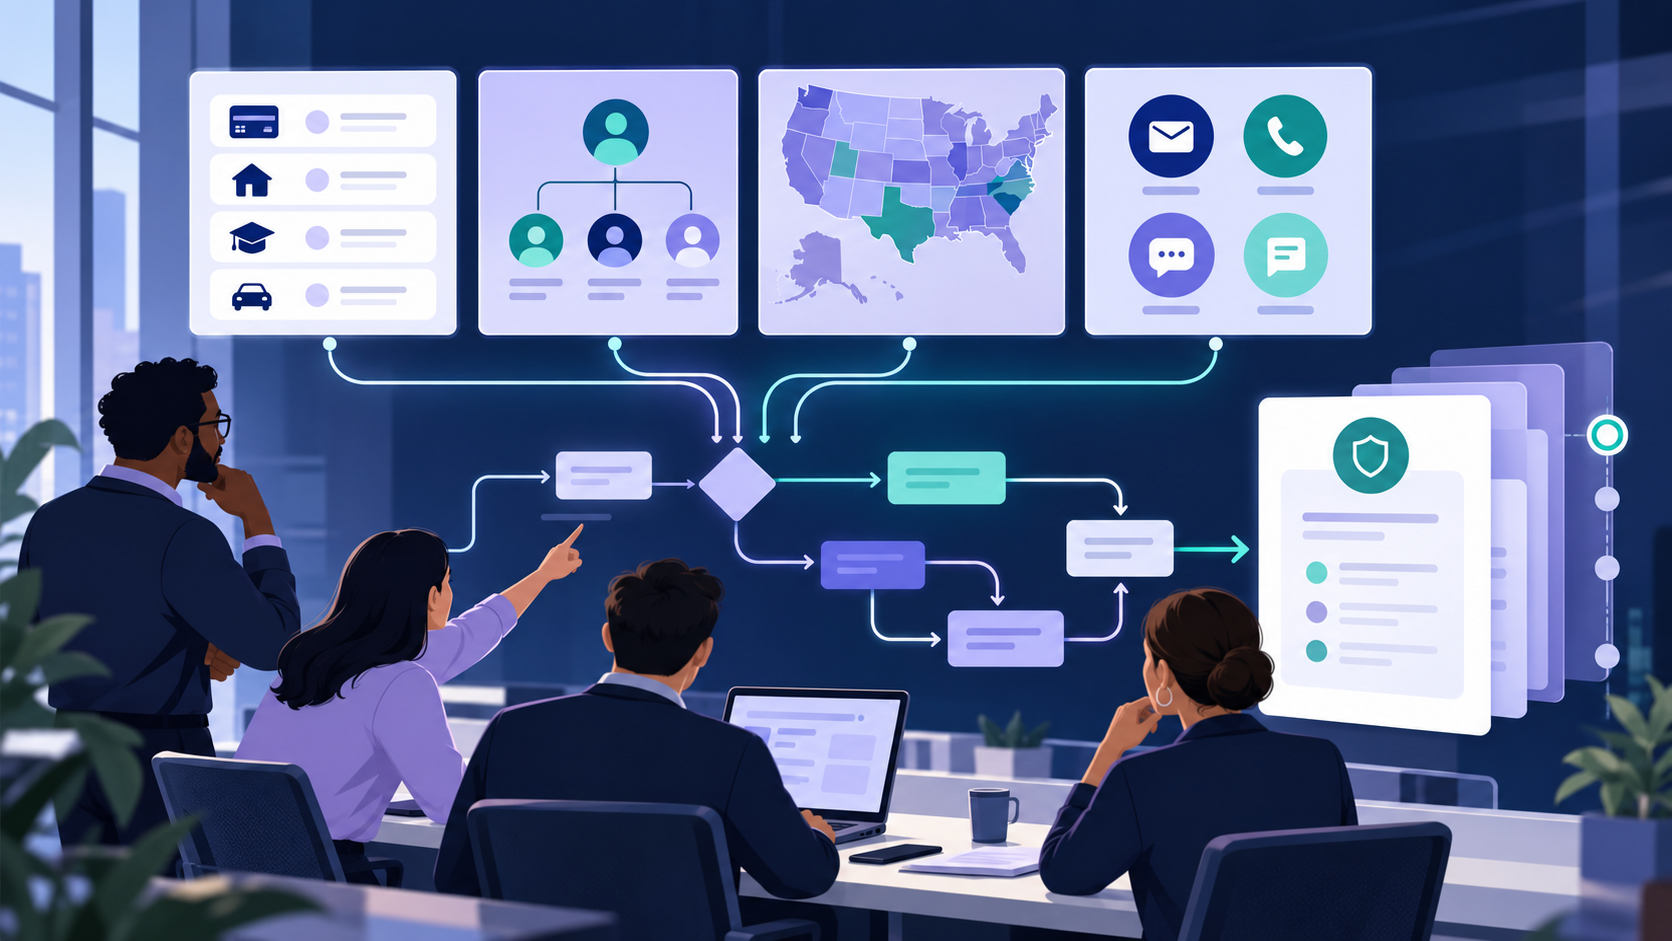
That scope map should be versioned. When an account, vendor, channel, or law changes, the operation needs a named owner to review and approve the affected strategy rather than silently inheriting an old rule set.
| Control point | What the workflow should do | Evidence for operations review |
|---|---|---|
| Rule applicability | Identify debt type, creditor and collector roles, account stage, jurisdiction, channel, and relevant policy before selecting an action. | Approved applicability map, effective date, policy owner, and rule version. |
| Pre-contact gate | Confirm usable account facts, recipient and channel permissions, contact preferences, suppression flags, permitted time, cadence, and opt-out status. | Data snapshot, check results, contact history, timestamp, and rule version. |
| Bounded action | Use approved content and verified account facts. Offer only payment or settlement options within delegated authority. | Template or action ID, rendered message or transcript, offer limits, and approval history. |
| Response and exception | Route opt-outs, disputes, wrong-party signals, complaints, hardship, representation notices, and uncertainty to a defined suppression, pause, or review path. Apply written-dispute triggers under the relevant rule set. | Original signal, receipt channel and time, action taken, queue owner, handoff context, and resolution. |
| Monitoring and change | Test edge cases, review outcomes, approve configuration changes, and retain a rollback path. | Test results, approvals, exception trends, version history, and remediation record. |
What should a controlled AI collection workflow look like?
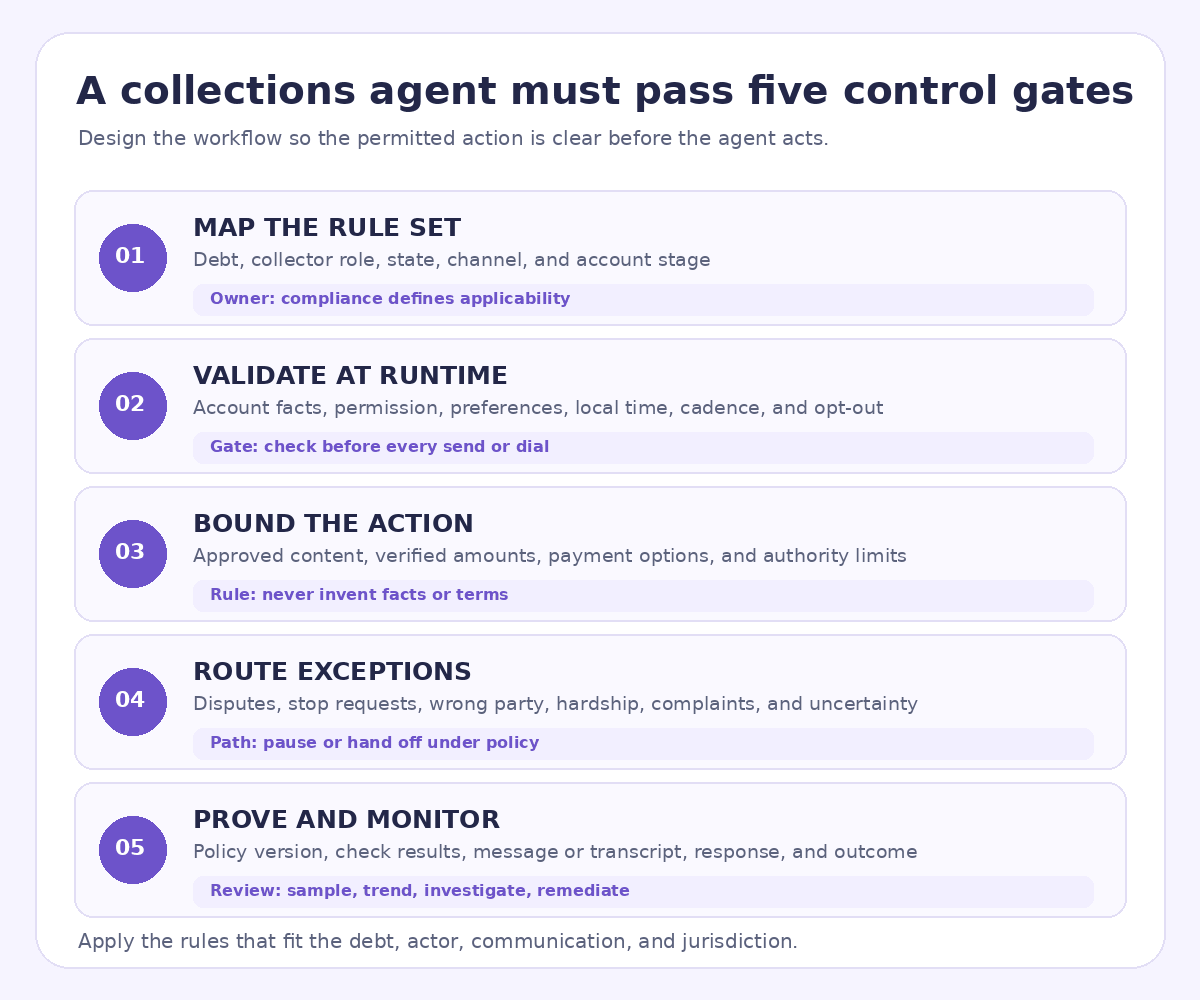
A controlled workflow uses gates for rule applicability, runtime permissions, allowed actions, exception routing, and audit evidence. Each gate must affect the action in time. A rule stored in a policy manual but missing from the dialer, messaging workflow, or vendor integration cannot block an ineligible contact.
What should the system check before every send or dial?
Run the relevant checks against the current account record at the moment of contact. Verify the recipient, channel, contact preferences, suppressions, available consent where required, local time, prior attempts, and rule version. Apply the rule set for that account and channel. Never carry a telephone call-frequency threshold into text or email logic. Enforce any stricter state, contractual, or internal limits that apply.
If a critical input is missing, stale, or contradictory, the workflow should block the action or send it to review. It should not guess which record is correct.
What should the agent be allowed to say or offer?
Use approved content for disclosures, balances, due dates, payment status, and other account facts. Let the model interpret intent and choose an allowed response, but source factual and legal statements from verified records and approved language.
Payment arrangements need explicit limits. Define which plans the agent may present, whether it can negotiate within a preapproved matrix, what requires approval, and which statements it must never make. The agent should not invent a deadline, legal consequence, balance, or settlement term.
For examples of capabilities to inspect during procurement, use the enterprise AI collections software evaluation guide. It is a buyer’s checklist, not a legal applicability analysis.
How should the workflow handle consumer responses?
“Stop texting,” “I dispute this,” “wrong person,” “I have an attorney,” and “I cannot pay because…” should activate defined workflow logic. Depending on the signal and applicable policy, the system may suppress a channel, pause an account for review, update a record, or route the case to a trained employee.
For a covered debt collector, a written dispute received during the validation period generally pauses collection on the debt or disputed portion until verification or a judgment is sent. A verbal dispute still deserves defined review, but the specific written-dispute trigger depends on the applicable rule. Record the original message, receipt time, validation status, and action taken.
A handoff should carry forward the account snapshot, contact history, message or transcript, and reason for escalation. That gives the reviewer enough context to act without asking the consumer to repeat the same information.
Where should human authority remain explicit?
A human should own legal interpretation and policy changes. Define the situations that require human review, such as uncertain identity, a dispute, a complaint, hardship, a legal threat, an exception to payment authority, or low-confidence output. These are prudent operating controls; whether a specific law mandates a pause or particular human step depends on the facts and applicable requirements.
Collections leaders can also review why human oversight matters in AI-driven debt recovery. The key operational test is whether the person receiving an escalation has authority, context, and a clear next action.
How can Strategy Builder make guardrails operational?
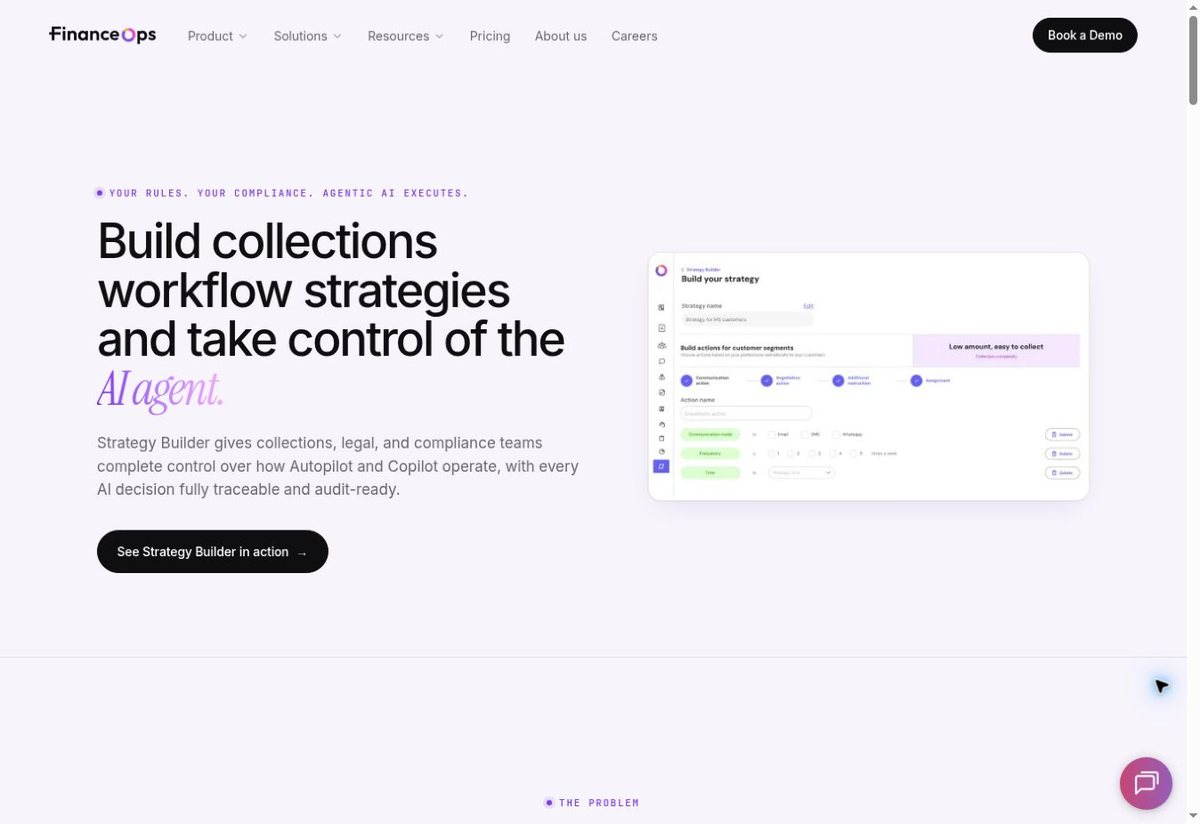
A strategy builder can give operations and compliance teams a place to configure approved segments, contact cadence, channels, message rules, negotiation boundaries, stop conditions, and escalation paths. The important buyer question is whether those settings are enforced in the workflow and reflected in an event record, not whether the product screen contains a control.
FinanceOps Strategy Builder describes configurable collection workflows. Evaluate any implementation against your approved policies, test cases, system integrations, and evidence needs. Product features alone do not establish that a specific deployment satisfies every applicable law.
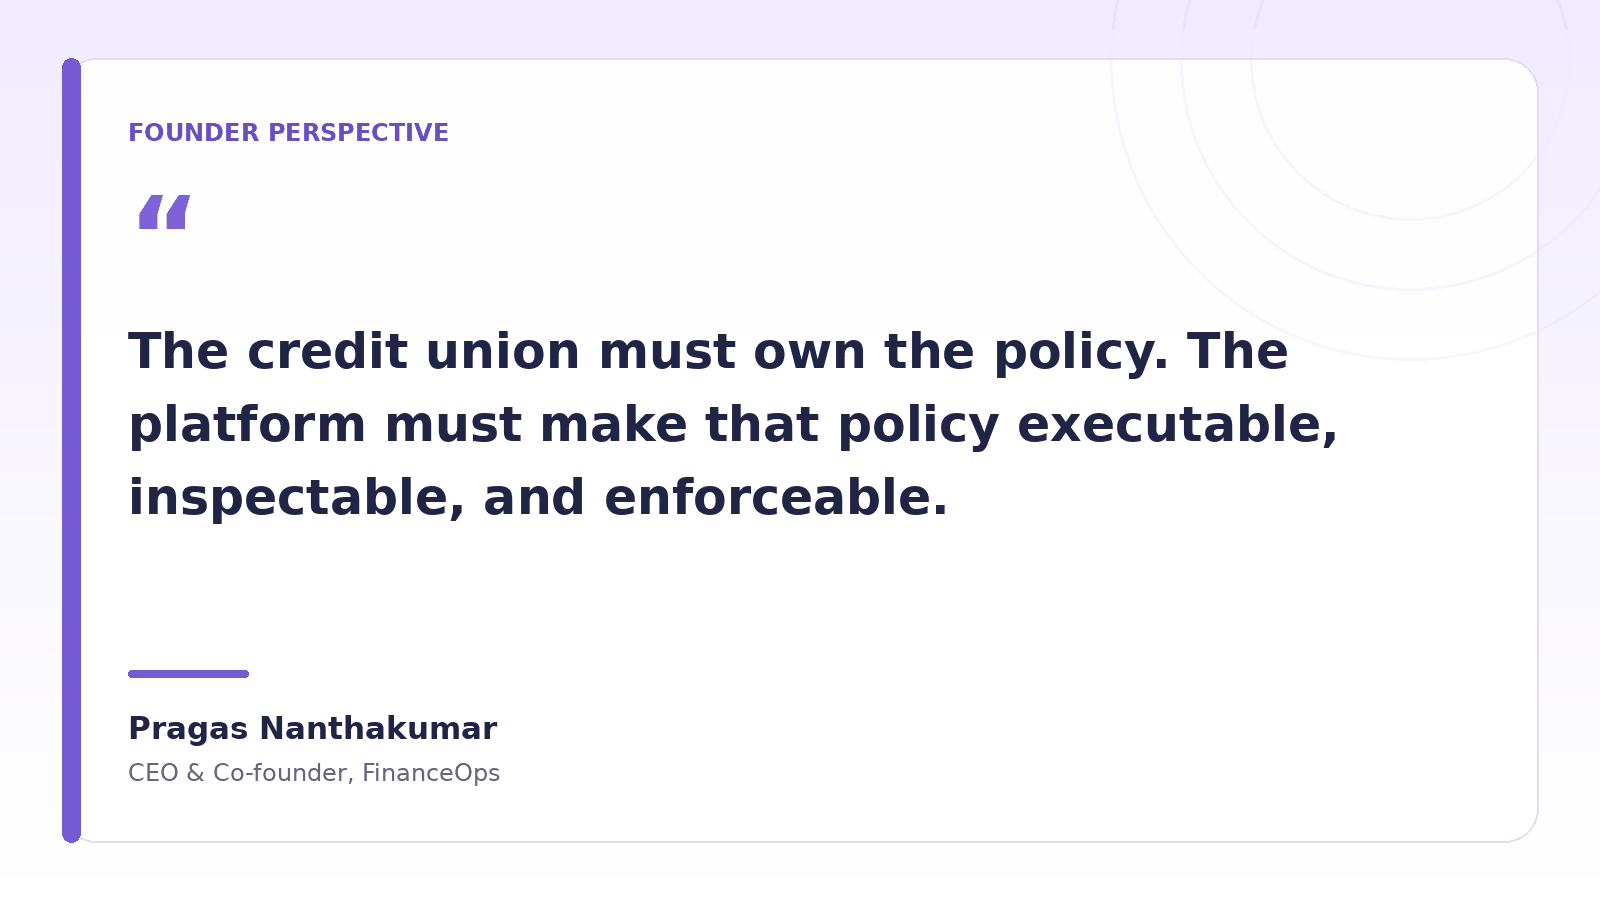
This founder perspective is from Pragas Nanthakumar’s article, Why Agentic AI Is the Future of Accounts Receivable.
How should a collections team test AI controls before launch?
Test the complete path from account data to contact and follow-up, not only whether the agent can produce a polished answer.
- Confirm who owns each decision. Document who approves legal mappings, channel rules, templates, payment authority, vendor changes, exceptions, and release decisions.
- Build a scenario set. Include stale balances, conflicting identity fields, consumer opt-outs, channel preferences, prior calls made by another team or vendor, disputes, wrong-party replies, hardship, complaints, and system outages.
- Check both allowed and blocked actions. Measure whether eligible outreach proceeds and prohibited or uncertain outreach is stopped or routed correctly. Test the same account across channels.
- Use a monitored pilot. Start with a bounded portfolio and human review. Compare AI decisions with policy expectations, investigate every material deviation, and require approval before expanding scope.
- Monitor consumer and control outcomes. Track blocked-contact rate, wrong-party contacts, opt-out processing time, complaint trends, escalation quality, policy deviations, repeat contacts, and resolved accounts. Recovery performance matters, but it should not hide a control failure.
- Govern changes. Version strategies, prompts, templates, models, and integrations. Test changes before release and keep a rollback path.
The NIST AI Risk Management Framework can serve as a voluntary structure for organizing governance, mapping, measurement, and management work. It is not a collections law or a certification of compliance.
For a closer look at platform governance and operational fit, compare agentic AI collections software with traditional platforms.
What should a compliance leader ask an AI collections vendor?
Ask the vendor to demonstrate the controls on a realistic account, including the failure paths.
- Which account facts and legal inputs must be present before the agent can act?
- Can the operation restrict each agent to an approved list of actions, channels, and offers?
- How does the system handle an opt-out, dispute, wrong-party answer, complaint, or uncertain identity?
- Can the system account for contact attempts made by staff and other vendors?
- What does an auditor see for the policy version, input data, decision, communication, and escalation?
- Who can change a strategy, how is that change approved, and how is rollback tested?
- Can the pilot block uncertain actions and measure control outcomes before automation expands?
FinanceOps’ compliance overview and Strategy Builder describe the product controls teams can evaluate. Map those controls to your own account types, legal obligations, and internal policies before deployment.
This article is general information, not legal advice. FDCPA and Regulation F applicability depends on the debt, the parties, the conduct, the channel, and other facts. Have qualified counsel review the requirements for your program.